- Hackers tricked an ASOS worker into handing over login details, then used them to break into outside platforms.
- The breach exposed customer names, contact details, and other account information. ASOS says passwords and card details stayed safe.
- Users on X reacted with jokes and worry after hackers used the ASOS app itself to announce the breach.
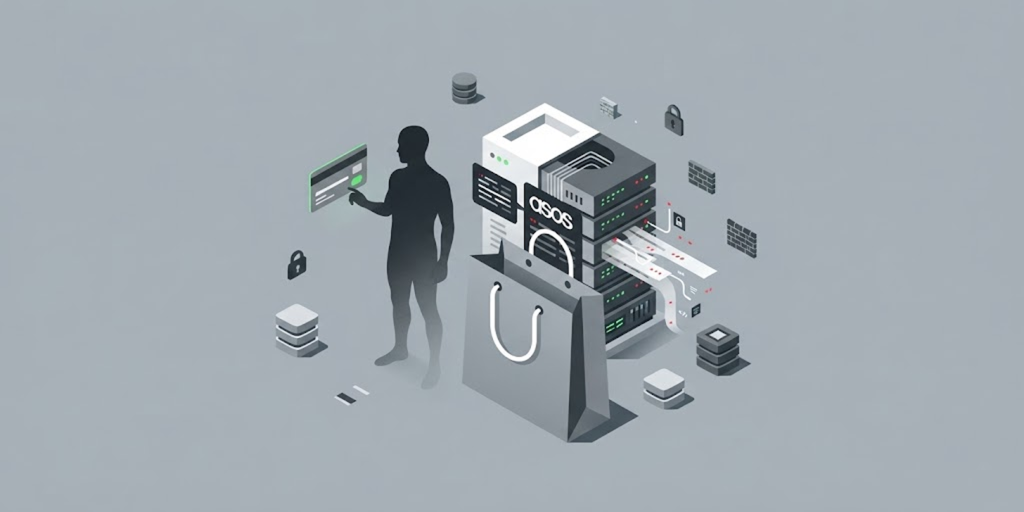
ASOS has confirmed that hackers broke into its systems through a clever trick. The attackers pretended to be someone the company trusted. This fooled a worker into giving up their login details. The hackers then used those details to enter outside platforms linked to ASOS.
The British fashion retailer shared this update with customers on October 8, 2026. ASOS acted fast once it noticed the problem. The company cut off access to the affected platforms right away. It also brought in cybersecurity experts, both from inside and outside the company. Police and other authorities joined the investigation too, according to Reuters.
How the Hackers Broke In
This kind of attack is called social engineering. It does not rely on breaking through firewalls or writing clever code. Instead, it relies on tricking a real person.
Social engineering has also played a role in wider tech-support fraud schemes, including the case involving two former executives who pleaded guilty over Telecom services used in a global Tech-support fraud scheme. The hacker pretends to be someone familiar. Once the worker trusts them, they hand over the keys without realizing it.
In this case, the trick worked. The stolen login let hackers reach systems ASOS uses outside its own network. These are called third-party platforms. Many big companies use them to store or manage customer data.
The breach first came to light on October 6. ASOS customers received a strange push notification through the company’s own app. The message claimed hackers had broken into an ASOS data system called Snowflake. It pointed users toward a Telegram channel. A group calling itself “Xuanye Group” posted the message and threatened to leak stolen data, as reported by ITV News.
ASOS has not confirmed everything the hackers claimed. Snowflake, the platform named in the threat, says it found no proof that its own system was broken into, according to The Guardian. The full picture is still forming as the investigation continues.
The Information at Risk
ASOS says the stolen information includes customer names and contact details. Some non-personal account information was also accessed. The company insists that payment card numbers and account passwords stayed safe throughout the breach.
However, The Guardian’s reporting adds more detail. It states the exposed data likely included delivery addresses, email addresses, and phone numbers. Recent search histories on the ASOS app may have been exposed as well. These details reportedly fall under the account information ASOS already mentioned in its own statement.
This mix of details raises concern beyond the breach itself. Criminals could use shopping habits and contact information to build convincing scam messages. A fake message that mentions your recent searches feels far more real than a random one.
ASOS has urged customers to stay alert. The company says it will never ask for passwords or payment details through unexpected messages. It recommends treating unsolicited calls, texts, or emails with caution, especially ones claiming to come from ASOS, as noted in Infosecurity Magazine’s coverage of the incident.
ASOS has not shared how many customers were affected. The investigation remains active, and the company says it has added new security steps to lower the risk of a repeat incident. Its full regulatory update is available through the London Stock Exchange’s RNS filing.
Reactions Pour in Online
The breach quickly became a talking point on X. Many users found it strange that hackers chose to announce the hack through the ASOS app itself. Others focused less on the danger and more on their own shopping carts.
One user, @mglllx, joked about the irony of ASOS alerting its own users to the hack through its app, poking fun at how unusual the method felt, based on posts gathered by AOL. Another user, @JackLysaght_, jokingly asked whether the hackers could at least offer customers a discount code in exchange for the trouble.
A user going by @agneponx played along with the chaos, joking that it felt like their first day on the job as ASOS’s new data protection officer. User @anxiousgirl01 shared more personal frustration, joking about the timing since they had planned to place an order the same day the news broke.
These reactions show a mix of humor and genuine unease. Still, the exposure of personal shopping data is a real risk. Criminals could use it to craft messages that look like they come directly from ASOS.
For now, the investigation continues. ASOS says it will share more updates if major new details come to light. Customers are advised to watch their accounts closely and avoid clicking links in unexpected messages claiming to be from the retailer.